[Nexus9K] VXLAN EVPN サービスチェイニング – GPO & ePBRを試してみた
前回は、VXLAN EVPN環境のマルチテナント上でエンドポイント間のセキュリティを実現する、Cisco NexusのGPO(Group Policy Option)を紹介しました。
前回記事:[Nexus9K] VXLAN EVPN セキュリティ – GPO(Group Policy Option)を試してみた
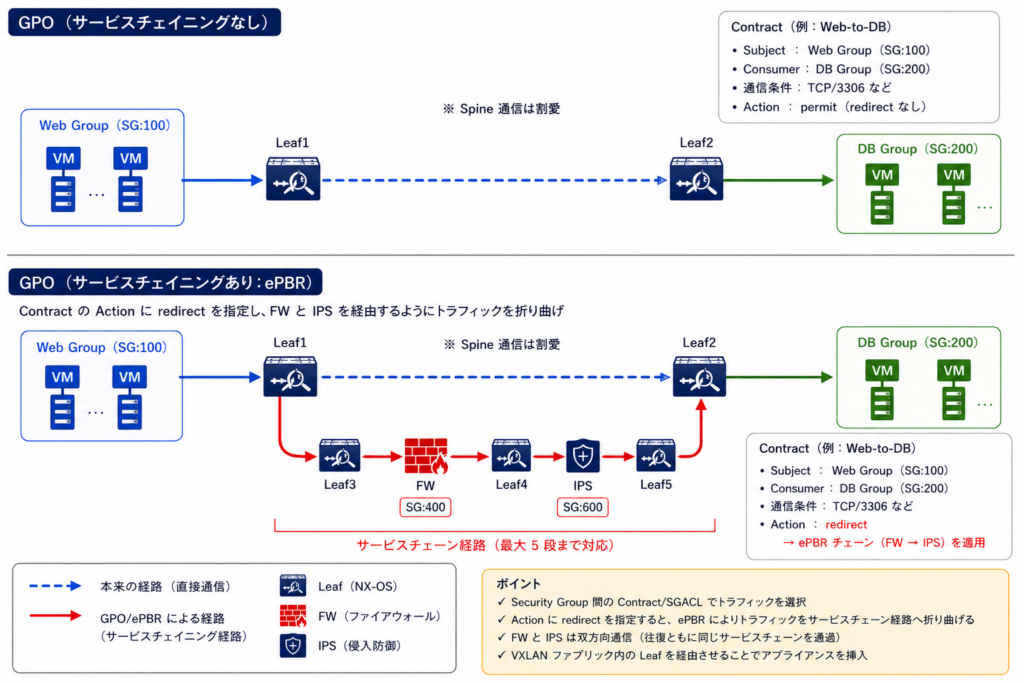
このGPOは、ePBRと組み合わせてサービスチェイニングを行うこともできます。たとえば次のように、特定のグループ間の通信だけにサービス装置を挟み込むことが可能です。
- Web→DBの通信だけをFWとIPSに通す
- テナント間の通信を共通のFWに集約する
- 外部公開系の通信をLB→FWの順に通す
- NAT装置を経路上に挿入する
本記事では、GPO+ePBRによるサービスチェイニングの動作概要を整理し、実機で簡単な動作を確認してみます。結論としては、ワンアーム接続のFWを経由させるシンプルな構成で、想定どおりEPG間の通信がFWを経由することを確認できました。
参考ドキュメント:Securing Data Centers with Microsegmentation and VXLAN GPO(Cisco White Paper)
GPO+ePBRを使ったサービスチェイニングとは
GPOを使ったサービスチェイニングでは、VXLANファブリックに接続されるサーバーやアプリケーションを「Web」「App」「DB」などのグループに分類し、グループ間の通信にFW、IPS、LBなどのサービスを差し込みます。
送信元・宛先のIPアドレスではなく、ワークロードの役割(グループ)で制御できるため、VMの移動やIPアドレスの変更があってもポリシーを維持しやすいのが特長です。E-W通信のマイクロセグメンテーションや、複数サイトへの展開にも向いています。
実際にトラフィックをサービス装置へ転送するのは、NexusのePBR(Enhanced Policy-Based Redirect)です。ePBRは、対象のトラフィックをサービス装置へリダイレクトし、サービスの順序制御、死活監視、負荷分散、障害時のDrop/Bypassなどを担う転送エンジンです。
| 従来のePBR | GPO+ePBR | |
|---|---|---|
| 対象トラフィックの選び方 | ACL(IPアドレスやポート) | 送信元・宛先のセキュリティグループ(SGT)と通信条件 |
| ポリシーの適用場所 | 入口インタフェース | VRF配下のsecurity contract |
| トポロジーへの依存 | IPアドレスや物理・論理トポロジーに依存しやすい | グループ単位なので、接続位置やIPの変更に強い |
つまり、GPOのsecurity contractで「どのグループ間の通信か」を選び、そのアクションとしてePBRのサービスチェーンを呼び出すことで、サービスチェイニングを実現しています。
検証内容と結果
EPG(Endpoint Group)間の通信を、リーフにワンアーム接続したサービス用EPG(FW)経由にするテストを行いました。前回のGPO検証の構成をベースにしています。
検証構成
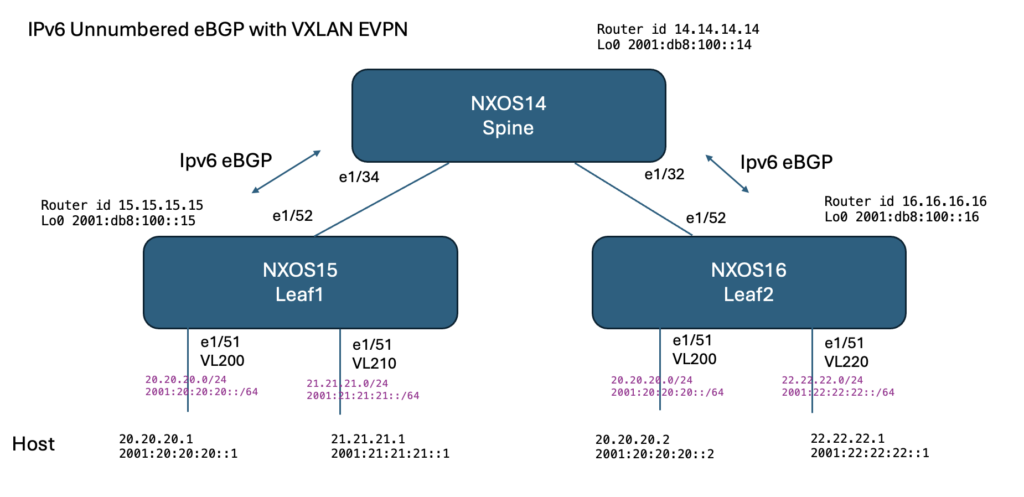
シングルテナント構成で、All IPv6 eBGP構成がベースです。
各リーフに接続したEPGを、異なる条件(IPv4/IPv6/VLAN/インタフェース)で定義しています。前回のGPO検証環境を使い回しているため、図中の「使わない」EPGは前回使用したもので、今回のテストでは使用していません。
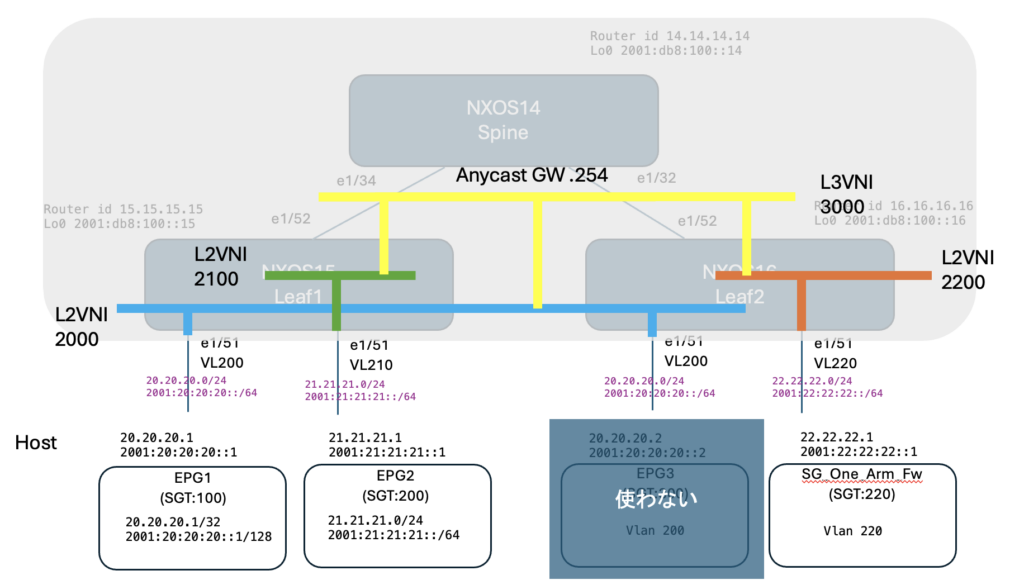
| グループ | SGT | リーフ | 分類条件 | 役割 |
|---|---|---|---|---|
| EPG1 | 100 | NXOS15 | IPv4 20.20.20.1/32、IPv6 2001:20:20:20::1/128 | 送信元 |
| EPG2 | 200 | NXOS15 | IPv4 21.21.21.0/24、IPv6 2001:21:21:21::1/128 | 宛先 |
| SG_One_Arm_Fw | 220 | NXOS16 | インタフェース Vlan220(type layer4-7) | サービス(ワンアームFW:22.22.22.1 / 2001:22:22:22::1) |
テスト内容
下図のとおり、EPG1からEPG2への通信がFWを経由するように設定し、想定どおりに動作するかを確認しました。
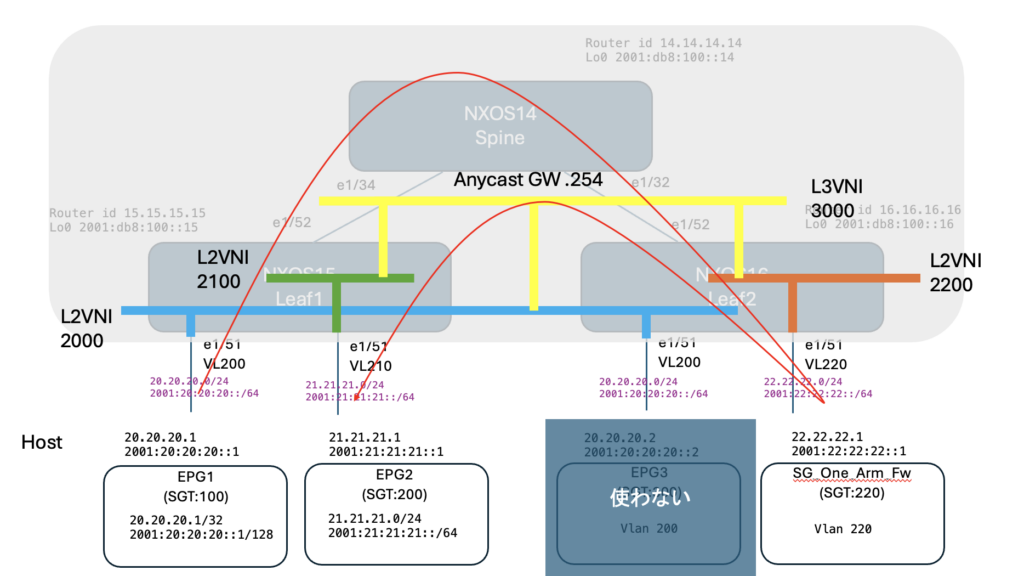
あわせて、ePBRのICMP Probeでサービス(FW)の死活監視が動作していることも確認しています。Probeの送信元として各リーフにLoopbackインタフェースを作成し、サービスチェイニングするEPGと同じVRFに所属させます。各リーフは、このLoopbackからサービスのエンドポイントに対してICMPでProbeを送ります。
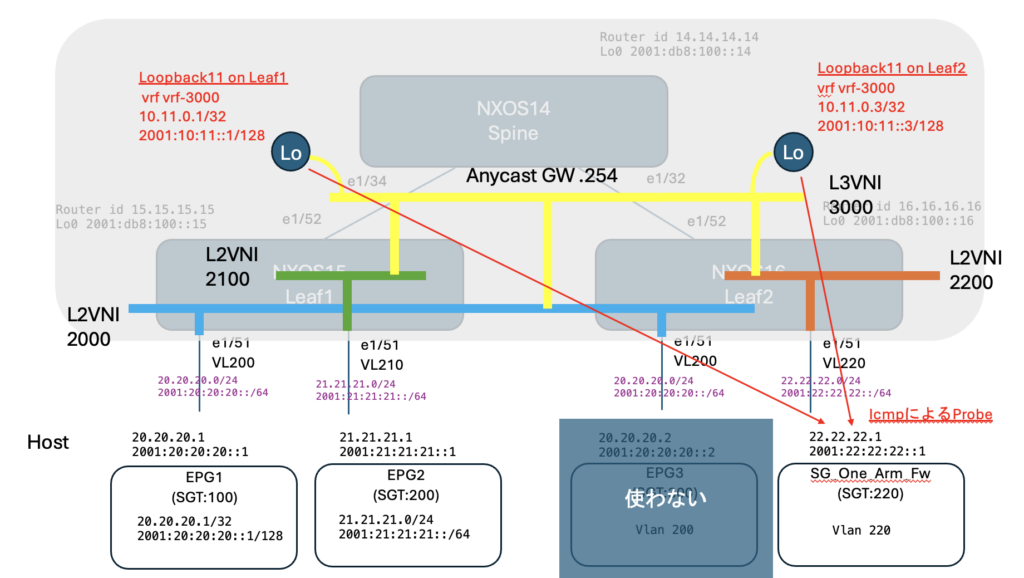
テスト結果
EPG1−EPG2間の通信が想定どおりFWを経由することを、各リーフのインタフェースカウンタで確認できました。ICMP ProbeによるサービスのステータスもUPになっています。ここからは、コンフィグとステータスを順に見ていきます。
GPO+ePBR関連のコンフィグ
設定は大きく、「機能の有効化」「EPGの定義」「Probe用Loopbackの作成」「ポリシーとePBRの定義」の4ステップです。GPO部分は前回の記事と同じ考え方です。
ステップ1:機能の有効化(NXOS15/16)
feature security-group
feature sla sender
feature pbr
feature epbr

system routing template-security-groupsGPOに加えて、ePBR(feature pbr / feature epbr)と、Probeに使うIP SLA(feature sla sender)を有効にします。system routing template-security-groups の反映には再起動が必要です。
ステップ2:EPGの定義
EPGは、エンドポイントが接続されている各リーフで定義します。FWのようなサービス装置用のグループは、type layer4-7 を指定して作成します。
! NXOS15
security-group 100 name EPG1
  match connected-endpoints vrf vrf-3000 ipv4 20.20.20.1/32
  match connected-endpoints vrf vrf-3000 ipv6 2001:20:20:20::1/128
security-group 200 name EPG2
  match connected-endpoints vrf vrf-3000 ipv4 21.21.21.0/24
  match connected-endpoints vrf vrf-3000 ipv6 2001:21:21:21::1/128

! NXOS16
security-group 220 name SG_One_Arm_Fw
  type layer4-7
  match interface Vlan220
ステップ3:Probe用Loopbackの作成
ICMP Probeの送信元となるLoopbackを、サービスと同じVRF(vrf-3000)に作成します。
! NXOS15
interface loopback11
  description SLA Probe loopback interface
  vrf member vrf-3000
  ip address 10.11.0.1/32 tag 12345
  ipv6 address 2001:10:11::1/128 tag 12345

! NXOS16
interface loopback11
  description SLA Probe loopback interface
  vrf member vrf-3000
  ip address 10.11.0.3/32 tag 12345
  ipv6 address 2001:10:11::3/128 tag 12345
ステップ4:ポリシーとePBRの定義(NXOS15/16共通)
設定は次の順につながっています。
- epbr service:サービス(FW)のエンドポイント、所属するセキュリティグループ(220)、Probeの方法を定義
- epbr service-chain:どのサービスをどの順番で通すかを定義(今回はFW 1台のみ)
- class-map / policy-map:対象の通信(ICMP)と、アクションとしてのservice-chainを定義
- security contract:VRF配下で「送信元EPG100 → 宛先EPG200」にpolicy-mapを適用
なお、ポリシー関連の設定名はGPOのホワイトペーパーをベースにしています。ホワイトペーパーは「HTTPサーバー宛てのWebトラフィックをFWに折り曲げる」前提のため、今回のICMPの検証とは名前が合っていない点はご容赦ください。
class-map type security match-any icmp
  match ip icmp
  match ipv6 icmpv6
class-map type security match-any web_icmp
  match ip icmp
class-map type security match-any web_icmp-v6
  match ipv6 icmpv6
policy-map type security HTTPs_Redirect_To_Fw
  class web_icmp
    log
    service-chain SRV_Chain_One_Arm_Fw
policy-map type security HTTPs_Redirect_To_Fw-v6
  class web_icmp-v6
    log
    service-chain SRV_Chain_One_Arm_Fw-v6
policy-map type security permit_icmp
  class icmp
    log

epbr service SRV_One_Arm_Fw-v6
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ipv6 2001:22:22:22::1

epbr service SRV_One_Arm_Fw
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ip 22.22.22.1

epbr service-chain SRV_Chain_One_Arm_Fw-v6
  10 set service SRV_One_Arm_Fw-v6

epbr service-chain SRV_Chain_One_Arm_Fw
  10 set service SRV_One_Arm_Fw

vrf context vrf-3000
  vni 3000
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw-v6
  security enforce tag 9999 default deny
IPv4とIPv6でサービス(service-end-point)を分けて定義し、それぞれ別のservice-chainとpolicy-mapで呼び出しています。
全体コンフィグ
全体コンフィグです(機器名をクリックすると展開されます)。NXOS15とNXOS16の太字部分が、上で説明したGPO+ePBRの設定です。NXOS14はSpineのため、GPOやePBRの設定はありません。
NXOS14(Spine)
NXOS14# show run

version 10.6(2) Bios:version 05.53
hostname NXOS14

<snip>

feature nxapi
nv overlay evpn
feature ospf
feature bgp
feature pim
feature grpc
feature netflow
feature analytics
feature lldp
clock timezone JST 9 0
clock protocol ptp vdc 1
feature nv overlay
feature ngoam
feature telemetry
feature nxsecure

<snip>

route-map NEXT-HOP-UNCH permit 10
  set ip next-hop unchanged
  set ipv6 next-hop unchanged

<snip>

interface Ethernet1/32
  description to NXOS16 Ethernet1/1
  ipv6 address use-link-local-only
  ipv6 nd ra-interval 4 min 3
  ipv6 nd ra-lifetime 10
  no shutdown

<snip>

interface Ethernet1/34
  description to NXOS15 Ethernet1/1
  ipv6 address use-link-local-only
  ipv6 nd ra-interval 4 min 3
  ipv6 nd ra-lifetime 10
  no shutdown

<snip>

interface loopback0
  description SPINE_LOOPBACK
  ipv6 address 2001:db8:100::14/128
icam monitor scale

line console
line vty
boot nxos bootflash:/nxos64-cs.10.6.2.F.bin
router bgp 65000
  router-id 14.14.14.14
  bestpath as-path multipath-relax
  address-family ipv6 unicast
    network 2001:db8:100::14/128
  address-family l2vpn evpn
    retain route-target all
  neighbor Ethernet1/32
    remote-as 65016
    description BGP_UNNUMBERED_TO_NXOS16
    address-family ipv6 unicast
    address-family l2vpn evpn
      send-community
      send-community extended
      route-map NEXT-HOP-UNCH out
  neighbor Ethernet1/34
    remote-as 65015
    description BGP_UNNUMBERED_TO_NXOS15
    address-family ipv6 unicast
    address-family l2vpn evpn
      send-community
      send-community extended
      route-map NEXT-HOP-UNCH out
NXOS15(Leaf1)
NXOS15# show run

version 10.6(3) Bios:version 01.12
hostname NXOS15

<snip>

feature nxapi
cfs eth distribute
nv overlay evpn
feature ospf
feature bgp
feature pim
feature grpc
feature pbr
feature interface-vlan
feature vn-segment-vlan-based
feature netflow
feature analytics
feature lacp
feature dhcp
feature lldp
clock timezone JST 9 0
clock protocol ptp vdc 1
feature sla sender
feature nv overlay
feature security-group
feature ngoam
feature telemetry
feature epbr
feature nxsecure

<snip>

security-group 100 name EPG1
  match connected-endpoints vrf vrf-3000 ipv4 20.20.20.1/32
  match connected-endpoints vrf vrf-3000 ipv6 2001:20:20:20::1/128
security-group 200 name EPG2
  match connected-endpoints vrf vrf-3000 ipv4 21.21.21.0/24
  match connected-endpoints vrf vrf-3000 ipv6 2001:21:21:21::1/128

class-map type security match-any icmp
  match ip icmp
  match ipv6 icmpv6
class-map type security match-any web_icmp
  match ip icmp
class-map type security match-any web_icmp-v6
  match ipv6 icmpv6
policy-map type security HTTPs_Redirect_To_Fw
  class web_icmp
    log
    service-chain SRV_Chain_One_Arm_Fw
policy-map type security HTTPs_Redirect_To_Fw-v6
  class web_icmp-v6
    log
    service-chain SRV_Chain_One_Arm_Fw-v6
policy-map type security permit_icmp
  class icmp
    log

fabric forwarding anycast-gateway-mac 2020.0000.00aa
ipv6 switch-packets lla
vlan 1,200,210,300
vlan 200
  vn-segment 2000
vlan 210
  vn-segment 2100
vlan 300
  vn-segment 3000

route-map RM_EVPN_NH permit 10
  set ipv6 next-hop 2001:db8:100::15

<snip>

vrf context vrf-3000
  vni 3000
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw-v6
  security enforce tag 9999 default deny
  rd auto
  address-family ipv4 unicast
    route-target import 3000:3000
    route-target import 3000:3000 evpn
    route-target export 3000:3000
    route-target export 3000:3000 evpn
  address-family ipv6 unicast
    route-target import 3000:3000
    route-target import 3000:3000 evpn
    route-target export 3000:3000
    route-target export 3000:3000 evpn
system routing template-security-groups

<snip>

interface Vlan200
  no shutdown
  vrf member vrf-3000
  ip address 20.20.20.254/24
  ipv6 address 2001:20:20:20::254/64
  fabric forwarding mode anycast-gateway

interface Vlan210
  no shutdown
  vrf member vrf-3000
  ip address 21.21.21.254/24
  ipv6 address 2001:21:21:21::254/64
  fabric forwarding mode anycast-gateway

interface Vlan300
  no shutdown
  vrf member vrf-3000
  ip forward
  ipv6 forward

interface nve1
  no shutdown
  host-reachability protocol bgp
  source-interface loopback0
  member vni 2000
    ingress-replication protocol bgp
  member vni 2100
    ingress-replication protocol bgp
  member vni 3000 associate-vrf

<snip>

interface Ethernet1/51
  description to VPC9
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 200,210
  no shutdown

interface Ethernet1/52
  description to NXOS14 Ethernet1/1
  ipv6 address use-link-local-only
  ipv6 nd ra-interval 4 min 3
  ipv6 nd ra-lifetime 10
  no shutdown

<snip>

interface loopback0
  description VTEP_LOOPBACK_IPV6
  ipv6 address 2001:db8:100::15/128

interface loopback11
  description SLA Probe loopback interface
  vrf member vrf-3000
  ip address 10.11.0.1/32 tag 12345
  ipv6 address 2001:10:11::1/128 tag 12345
icam monitor scale

line console
line vty
boot nxos bootflash:/nxos64-cs.10.6.3.F.bin
router bgp 65015
  router-id 15.15.15.15
  bestpath as-path multipath-relax
  address-family ipv6 unicast
    network 2001:db8:100::15/128
  address-family l2vpn evpn
  neighbor Ethernet1/52
    remote-as 65000
    description BGP_UNNUMBERED_TO_NXOS14
    address-family ipv6 unicast
    address-family l2vpn evpn
      send-community
      send-community extended
      route-map RM_EVPN_NH out
  vrf vrf-3000
    address-family ipv4 unicast
      network 10.11.0.1/32
      advertise l2vpn evpn
    address-family ipv6 unicast
      network 2001:10:11::1/128
      advertise l2vpn evpn
evpn
  vni 2000 l2
    rd auto
    route-target import 2000:2000
    route-target export 2000:2000
  vni 2100 l2
    rd auto
    route-target import 2100:2100
    route-target export 2100:2100

epbr service SRV_One_Arm_Fw-v6
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ipv6 2001:22:22:22::1

epbr service SRV_One_Arm_Fw
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ip 22.22.22.1

epbr service-chain SRV_Chain_One_Arm_Fw-v6
  10 set service SRV_One_Arm_Fw-v6

epbr service-chain SRV_Chain_One_Arm_Fw
  10 set service SRV_One_Arm_Fw
NXOS16(Leaf2)
NXOS16# show run
version 10.6(3) Bios:version 01.12
hostname NXOS16

<snip>

feature nxapi
cfs eth distribute
nv overlay evpn
feature ospf
feature bgp
feature pim
feature grpc
feature pbr
feature interface-vlan
feature vn-segment-vlan-based
feature netflow
feature analytics
feature lacp
feature dhcp
feature lldp
clock timezone JST 9 0
clock protocol ptp vdc 1
feature sla sender
feature nv overlay
feature security-group
feature ngoam
feature telemetry
feature epbr

<snip>

security-group 220 name SG_One_Arm_Fw
  type layer4-7
  match interface Vlan220
security-group 300 name EPG3
  match vlan 200
security-group 400 name EPG4
  match vlan 220
class-map type security match-any icmp
  match ip icmp
  match ipv6 icmpv6
class-map type security match-any web_icmp
  match ip icmp
class-map type security match-any web_icmp-v6
  match ipv6 icmpv6
policy-map type security HTTPs_Redirect_To_Fw
  class web_icmp
    log
    service-chain SRV_Chain_One_Arm_Fw
policy-map type security HTTPs_Redirect_To_Fw-v6
  class web_icmp-v6
    log
    service-chain SRV_Chain_One_Arm_Fw-v6
policy-map type security permit_icmp
  class icmp
    log

fabric forwarding anycast-gateway-mac 2020.0000.00aa
ipv6 switch-packets lla
vlan 1,200,220,300
vlan 200
  vn-segment 2000
vlan 220
  vn-segment 2200
vlan 300
  vn-segment 3000

route-map RM_EVPN_NH permit 10
  set ipv6 next-hop 2001:db8:100::16
service dhcp

<snip>

vrf context vrf-3000
  vni 3000
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw
  security contract source 100 destination 200 policy HTTPs_Redirect_To_Fw-v6
  security enforce tag 9999 default deny
  rd auto
  address-family ipv4 unicast
    route-target import 3000:3000
    route-target import 3000:3000 evpn
    route-target export 3000:3000
    route-target export 3000:3000 evpn
  address-family ipv6 unicast
    route-target import 3000:3000
    route-target import 3000:3000 evpn
    route-target export 3000:3000
    route-target export 3000:3000 evpn
system routing template-security-groups


interface Vlan1

interface Vlan200
  no shutdown
  vrf member vrf-3000
  ip address 20.20.20.254/24
  ipv6 address 2001:20:20:20::254/64
  fabric forwarding mode anycast-gateway

interface Vlan220
  no shutdown
  vrf member vrf-3000
  ip address 22.22.22.254/24
  ipv6 address 2001:22:22:22::254/64
  fabric forwarding mode anycast-gateway

interface Vlan300
  no shutdown
  vrf member vrf-3000
  ip forward
  ipv6 forward

interface nve1
  no shutdown
  host-reachability protocol bgp
  source-interface loopback0
  member vni 2000
    ingress-replication protocol bgp
  member vni 2200
    ingress-replication protocol bgp
  member vni 3000 associate-vrf

<snip>

interface Ethernet1/51
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 200,220
  no shutdown

interface Ethernet1/52
  speed 40000
  no negotiate auto
  ipv6 address use-link-local-only
  ipv6 nd ra-interval 4 min 3
  ipv6 nd ra-lifetime 10
  no shutdown

<snip>

interface loopback0
  description VTEP_LOOPBACK_IPV6
  ipv6 address 2001:db8:100::16/128

interface loopback11
  description SLA Probe loopback interface
  vrf member vrf-3000
  ip address 10.11.0.3/32 tag 12345
  ipv6 address 2001:10:11::3/128 tag 12345
icam monitor scale

line console
line vty
boot nxos bootflash:/nxos64-cs.10.6.3.F.bin
router bgp 65016
  router-id 16.16.16.16
  bestpath as-path multipath-relax
  address-family ipv6 unicast
    network 2001:db8:100::16/128
  address-family l2vpn evpn
  neighbor Ethernet1/52
    remote-as 65000
    description BGP_UNNUMBERED_TO_NXOS14
    address-family ipv6 unicast
    address-family l2vpn evpn
      send-community
      send-community extended
      route-map RM_EVPN_NH out
evpn
  vni 2000 l2
    rd auto
    route-target import 2000:2000
    route-target export 2000:2000
  vni 2200 l2
    rd auto
    route-target import 2200:2200
    route-target export 2200:2200

epbr service SRV_One_Arm_Fw-v6
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ipv6 2001:22:22:22::1

epbr service SRV_One_Arm_Fw
  vrf vrf-3000
  security-group 220
  probe icmp source-interface loopback11
  service-end-point ip 22.22.22.1

epbr service-chain SRV_Chain_One_Arm_Fw-v6
  10 set service SRV_One_Arm_Fw-v6

epbr service-chain SRV_Chain_One_Arm_Fw
  10 set service SRV_One_Arm_Fw
ステータス確認
GPOとePBRを中心にステータスを確認します。主に見るのは次の4つです。
| 確認したいこと | コマンド |
|---|---|
| サービスチェーンとサービスの状態 | show epbr service-chain |
| コントラクトとヒット数(アクションがredirectか) | show contracts |
| サービスのエンドポイントとProbeの状態 | show epbr service |
| ポリシーにマッチした実フロー | show logging ip access-list cache |
なお、IPv6関連の一部のコマンド出力で、表示が崩れる事象(IPv6アドレスの行がプロンプトの後ろに表示される)が見られました。出力はそのまま載せています。
サービスチェーンの状態:show epbr service-chain(NXOS15)
IPv4・IPv6とも、サービスチェーンとサービスのエンドポイントがUPになっています。障害時の動作(fail-action)はDrop、アクションはRedirectです。
NXOS15# show epbr service-chain

Service-chain : SRV_Chain_One_Arm_Fw  state:UP
    service:SRV_One_Arm_Fw, sequence:10, fail-action:Drop
      load-balance:Source-Destination-ipprotocol, action:Redirect
      state:UP
      IP 22.22.22.1 track 1 [UP]

Service-chain : SRV_Chain_One_Arm_Fw-v6  state:UP
    service:SRV_One_Arm_Fw-v6, sequence:10, fail-action:Drop
      load-balance:Source-Destination-ipprotocol, action:Redirect
      state:UP
NXOS15# V6 2001:22:22:22::1 track 2 [UP]
コントラクトの状態:show contracts
EPG100→EPG200のコントラクトのActionが redir,log となっており、Statsのカウントも増えています。両リーフでリダイレクトのポリシーにヒットしていることが分かります。
NXOS15# show contracts

VRF              SGT   DGT   Policy           Dir    Stats        Class            Action       OperSt
--------------------------------------------------------------------------------------------------------
vrf-3000         100   200   HTTPs_Redirect_To_Fw
                                              bidir  600          web_icmp         redir,log    enabled
                 100   200   HTTPs_Redirect_To_Fw-v6
                                              bidir  458          web_icmp-v6      redir,log    enabled

NXOS16# show contracts

VRF              SGT   DGT   Policy           Dir    Stats        Class            Action       OperSt
--------------------------------------------------------------------------------------------------------
vrf-3000         100   200   HTTPs_Redirect_To_Fw
                                              bidir  1600         web_icmp         redir,log    enabled
                 100   200   HTTPs_Redirect_To_Fw-v6
                                              bidir  887          web_icmp-v6      redir,log    enabled
サービスとProbeの状態:show epbr service
サービスのエンドポイント(22.22.22.1 / 2001:22:22:22::1)が、ICMP ProbeでUPと判定されています。出力が長いため、凡例部分は折りたたんでいます(NXOS15・NXOS16とも同じ内容です)。
show epbr service(NXOS15)
NXOS15# show epbr service
Legend:
Operational State (Op-STS):  UP:Reachable, DOWN:Unreachable,
                             SVC-ADMIN-DOWN:Service shut
                             ADMIN-DOWN:Admin shut, OPER-DOWN:Out-of-service
Probe:                       Protocol/Frequency(sec)/Timeout(sec)/Retry-Up-Count/Retry-Down-Count
Hold-down Threshold:         Count/Time(sec)
Service mode:                Full:Full-Duplex, Half:Half-Duplex
Type:                        L3:Layer-3, L2:Layer-2
Threshold:                   Value(percent)
Mode:                        A: Active, HS: Hot-Standby

Name                              Type      Service mode  VRF
==========================================================================================
SRV_One_Arm_Fw                    L3        Full          vrf-3000

Security-group    Reverse security-group   Threshold
=======================================================
220

Endpoint IP/Intf         Track SLA       Op-ST          Probe               Hold-down Role Weight
Reverse IP/Intf          Track SLA       Op-ST          Probe
=================================================================================================

22.22.22.1/              1     20001     UP             ICMP/0/0/0/0                  A    1

Name                              Type      Service mode  VRF
==========================================================================================
SRV_One_Arm_Fw-v6                 L3        Full          vrf-3000

Security-group    Reverse security-group   Threshold
=======================================================
220

Endpoint IP/Intf         Track SLA       Op-ST          Probe               Hold-down Role Weight
Reverse IP/Intf          Track SLA       Op-ST          Probe
=================================================================================================

NXOS15# 22:22::1/        2     20002     UP             ICMP/0/0/0/0                  A    1
show epbr service(NXOS16)
NXOS16# show epbr service
Legend:
Operational State (Op-STS):  UP:Reachable, DOWN:Unreachable,
                             SVC-ADMIN-DOWN:Service shut
                             ADMIN-DOWN:Admin shut, OPER-DOWN:Out-of-service
Probe:                       Protocol/Frequency(sec)/Timeout(sec)/Retry-Up-Count/Retry-Down-Count
Hold-down Threshold:         Count/Time(sec)
Service mode:                Full:Full-Duplex, Half:Half-Duplex
Type:                        L3:Layer-3, L2:Layer-2
Threshold:                   Value(percent)
Mode:                        A: Active, HS: Hot-Standby

Name                              Type      Service mode  VRF
==========================================================================================
SRV_One_Arm_Fw                    L3        Full          vrf-3000

Security-group    Reverse security-group   Threshold
=======================================================
220

Endpoint IP/Intf         Track SLA       Op-ST          Probe               Hold-down Role Weight
Reverse IP/Intf          Track SLA       Op-ST          Probe
=================================================================================================

22.22.22.1/              1     20001     UP             ICMP/0/0/0/0                  A    1

Name                              Type      Service mode  VRF
==========================================================================================
SRV_One_Arm_Fw-v6                 L3        Full          vrf-3000

Security-group    Reverse security-group   Threshold
=======================================================
220

Endpoint IP/Intf         Track SLA       Op-ST          Probe               Hold-down Role Weight
Reverse IP/Intf          Track SLA       Op-ST          Probe
=================================================================================================

NXOS16# 22:22::1/        2     20002     UP             ICMP/0/0/0/0                  A    1
実フローの確認:show logging ip access-list cache
EPG1(20.20.20.1 / 2001:20:20:20::1)とEPG2(21.21.21.x / 2001:21:21:21::1)の間のICMPがポリシーにマッチしています。NXOS16では、Src Intfが Ethernet1/51 と nve-peer1 の両方で記録されており、FWへ折り返された通信とファブリック経由の通信の両方を処理していることがうかがえます。
NXOS15# show logging ip access-list cache
Src IP            Dst IP            S-Port  D-Port  Src Intf             Protocol      Hits
---------------------------------------------------------------------------------------------
21.21.21.1        20.20.20.1        0       0       Ethernet1/51         (1)ICMP       0
2001:21:21:21::1  2001:20:20:20::1  0       0       Ethernet1/51         (58)IPv6-ICMP 0
2001:20:20:20::1  2001:21:21:21::1  0       0       Ethernet1/51         (58)IPv6-ICMP 0
20.20.20.1        21.21.21.1        0       0       Ethernet1/51         (1)ICMP       0

NXOS16# show logging ip access-list cache
Src IP            Dst IP            S-Port  D-Port  Src Intf             Protocol      Hits
---------------------------------------------------------------------------------------------
21.21.21.1        20.20.20.1        0       0       nve-peer1            (1)ICMP       0
21.21.21.1        20.20.20.1        0       0       Ethernet1/51         (1)ICMP       0
2001:21:21:21::1  2001:20:20:20::1  0       0       Ethernet1/51         (58)IPv6-ICMP 0
2001:20:20:20::1  2001:21:21:21::1  0       0       Ethernet1/51         (58)IPv6-ICMP 24
2001:20:20:20::1  2001:21:21:21::1  0       0       nve-peer1            (58)IPv6-ICMP 24
2001:21:21:21::1  2001:20:20:20::1  0       0       nve-peer1            (58)IPv6-ICMP 0
20.20.20.1        21.21.21.1        0       0       Ethernet1/51         (1)ICMP       0
20.20.20.1        21.21.21.1        0       0       nve-peer1            (1)ICMP       0
まとめ
今回は前回のGPOに続いて、ePBRと組み合わせたサービスチェイニングの動作を確認しました。
- グループ単位でサービスを挟み込める:security contractのアクションにservice-chainを指定するだけで、特定のEPG間の通信だけをFW経由にできました。
- 死活監視も組み込み済み:ePBRのICMP Probeでサービスの状態を監視し、障害時の動作(Drop/Bypass)も指定できます。
- IPv4/IPv6は別定義:サービスのエンドポイント、service-chain、policy-mapをアドレスファミリーごとに用意する必要があります。
今回はワンアームFWを前提にした基本的な動作のみの確認でしたが、ePBRには多段のサービスチェイニング、ツーアーム接続、サービスへの負荷分散など多様なオプションがあります。マルチテナント環境でも、サービスに応じて柔軟な構成が取れそうです。